How Small Teams Should Document Security Decisions So They Hold Up Later
Why verbal security decisions fail small teams at audits, insurance renewals, and disputes — and how a one-page decision record turns them into proof. Includes what belongs on each record, a filled-in example, a simple quarterly review rhythm, and the moments documentation pays for itself. Written from Grant Dorsey's first-person compliance experience with small U.S. offices.
After a decade of helping small offices prepare for insurance questionnaires, client audits, and the occasional pointed question from a bank or landlord, I can tell you what separates the offices that sleep easy from the ones that scramble: writing things down. Not thick binders of policy language — a thin folder of decisions that actually got recorded. A practical small business security compliance checklist looks less like a shopping list of tools and more like a log of judgment calls, each one dated, named, and explained in plain English.
Because that's what real security decisions are: judgment calls. Who gets admin rights, whether the after-hours cleaning crew uses your Wi-Fi or their own hotspot, how long the camera footage stays on the recorder, which laptops carry the managed agent and which ones are "just temporary." Every office makes these calls. Most of them happen in hallways and over lunch, verbally, and that's exactly where they go to die.
Why "We Talked About It" Is Not Proof
In every audit, insurance renewal, and dispute I've sat through, the phrase "we talked about it" carries the same weight as "we meant to." The person across the table — an auditor, an underwriter, a client's vendor-risk team — can't act on a memory they weren't part of. They can act on a dated note that says who decided, when, and why.
I remember helping an architecture firm answer a client's vendor questionnaire after a laptop had been stolen the previous year. The owner had done everything right in the moment: disabled the device, reset the accounts, changed the passwords. But none of it was written down, and by the time the questionnaire arrived, the person who could explain the sequence had left for another job. The firm spent days reconstructing a story that a half-page note, written at the time, would have told in a minute. That uncomfortable gap between what you did and what you can show is precisely the failure a small business security compliance checklist is meant to prevent.
Documentation like this isn't for lawyers. It's for future you — three hires, two software changes, and one forgotten password later.
What a One-Page Decision Record Contains
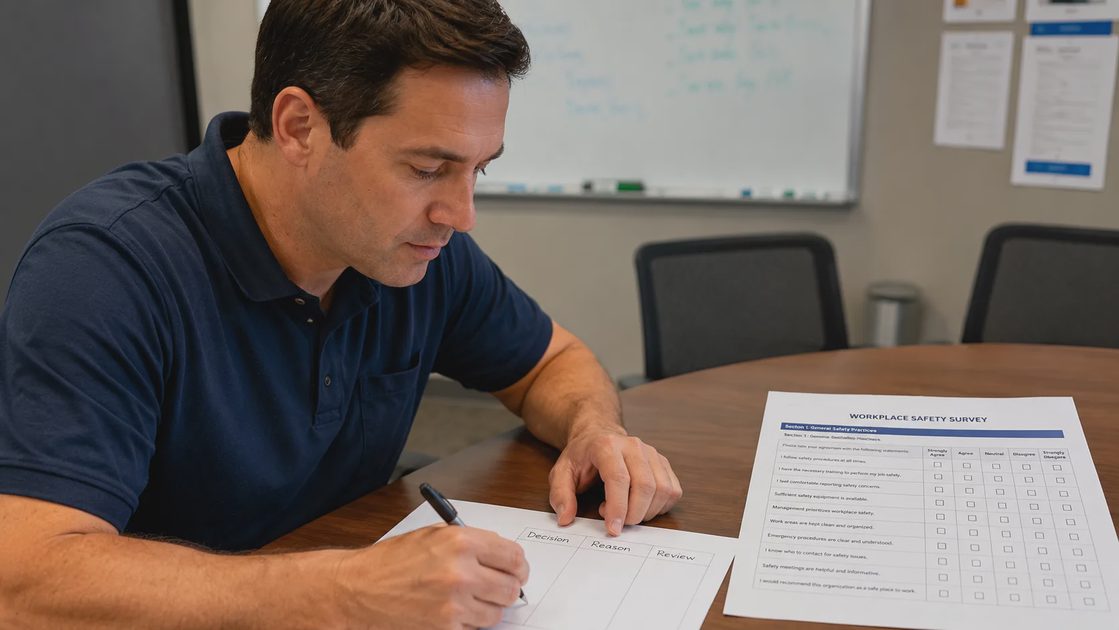
A decision record is not an essay and not a policy manual. It's one page that answers the questions a stranger would ask if they inherited your office tomorrow. Here is what belongs on it:
The decision, stated as a complete sentence: "All company laptops run our managed antivirus and must pass a scan before connecting to the office network."
Who made it and who was in the room, because "everyone agreed" doesn't survive a staff change.
The date and the trigger — the insurance renewal, the incident, the new contractor arrangement that started it.
The reason in plain language, including what you were reacting to.
What this decision replaced, or the note "new."
When it gets reviewed again, and by whom.
That last line is the one most templates skip, and it's the one that keeps records honest. A decision you never revisit becomes folklore; a decision with a review date becomes something you can update instead of defend.
A Filled-In Example
Here is roughly what a finished record looks like when it's done right — short enough to read in under a minute:
Field | What you might write | Why it works |
|---|---|---|
Decision | Guest devices join a separate Wi-Fi network, not the office one | Clear enough for anyone to follow |
Trigger | A contractor's laptop showed up on our office network with a scan alert | Explains why the rule exists |
Reason | Our shared office Wi-Fi password had been given to every visitor for years | The "why" that stops the rule being quietly reversed |
Review | Next review in March, owned by the office manager | Keeps the record alive instead of permanent |
Notice the record doesn't name a product or a version. That's deliberate. Software changes every year; the reasoning changes rarely. In my experience, teams that write the reason down make the decision last, while teams that only write the product name end up re-litigating it at every renewal cycle.
The Rhythm That Keeps Documentation Honest
A folder full of records is only as good as its review habit. The good news is that a small office doesn't need a calendar of audits — it needs one repeating appointment and a short agenda. The endpoint security for small business decisions you made when you bought the software are usually the ones that drift: who still has local admin, whether the agent runs on every machine, whether that "temporary" laptop ever got enrolled.
When I sit down with a team for the first review, I use the same four steps every time:
Open the folder or spreadsheet and read every record out loud. Two people is plenty.
Mark anything that still matches how the office actually works.
Update the rest on the spot — new date, new reason, same page.
If a decision got reversed informally, write that down too, with the reason, so the record matches reality.
File everything in one shared place with dates in the names — "2026-09-wifi-guest-policy" beats "final_v2_REAL." Email is not a filing system; over the years I've lost more records to inboxes than to hard drives.
The Moments the Folder Pays For Itself
Three moments make the folder pay for itself. The first is any questionnaire or audit, where written decisions turn a two-week scramble into a quiet afternoon. The second is an actual incident, when you have to explain afterward what was decided, when, and why. The third is the dispute — the employee who says nobody told them the laptop policy, or the vendor who claims your office never asked for the report.
Each of those conversations is easier when there is a piece of paper that predates the problem. Written records are the part of a small business security compliance checklist that never goes out of date, because the tools get replaced but the reasoning doesn't. That isn't compliance theater; it's the difference between defending a decision you remember and showing a decision you recorded.
I keep a running section in my Avoidable Problems notebook for the small offices I've watched struggle here, and the pattern is consistent: the ones that document their decisions treat it as a habit, not a project. Security gets easier when the rules make sense, and rules make sense when someone can still explain, a year later, why they exist. Start with one decision, one page, one date. The folder grows on its own.
What to Do If an Employee Laptop Brings Malware Into the Office Network
NextRansomware Panic Checklist: What Small Teams Should Do Before They Start Guessing
How to Build a Basic Device and Access Checklist Before Compliance Becomes a Crisis
A basic device and access checklist is the single most useful document i...
The 5 Security Policies Every Small Office Should Be Able to Show on Demand
Small offices do not need thick compliance binders; they need five short...
Your Antivirus Tool Won’t Save You From Bad Offboarding
A practical guide to why antivirus software cannot fix offboarding gaps:...
Leave a comment
No comments yet.